In today’s world, digital authentication is a cornerstone of IT security. Whether to protect personal data, ensure regulatory compliance or facilitate online transactions, it has become an essential part of our daily digital lives.
What is digital authentication?
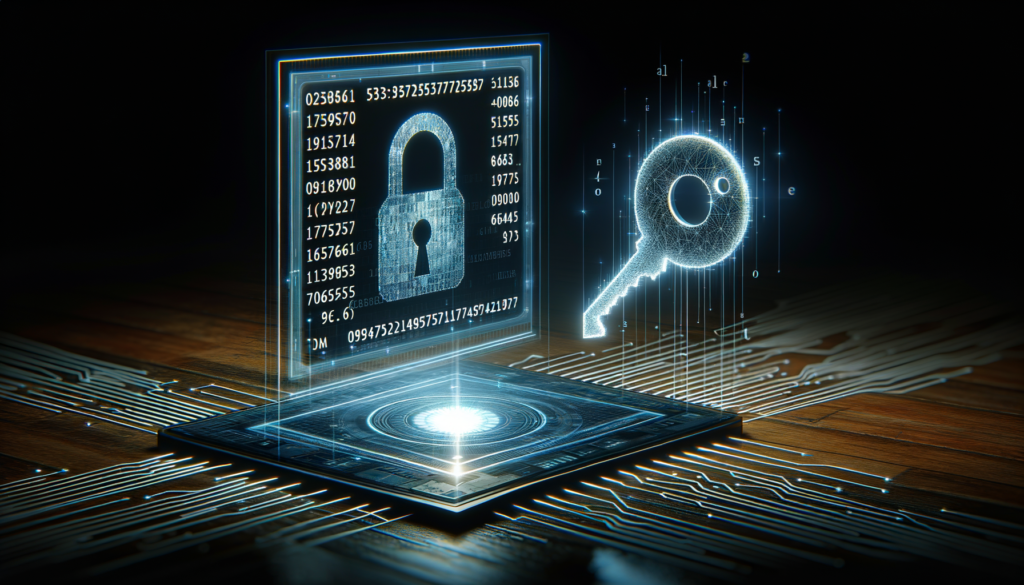
Digital authentication refers to the processes used to verify the identity of a user or device attempting to access an online system, application, or network. It generally relies on a combination of different factors, including something the user knows (such as a password), possesses (such as a smartphone), or is (such as fingerprints) to verify their identity with confidence. This classification follows that of the CNIL, which distinguishes between the knowledge factor (what one knows), the possession factor (what one has), and the inherent factor (what one is, which may be biometric or behavioral); according to this authority, authentication is classified as multi-factor when it combines at least two of these distinct categories, and as robust when it is based on a cryptographic mechanism deemed secure, such as a cryptographic key (CNIL, “Security: Authenticating Users,” March 14, 2024).
Common authentication methods
There are several authentication methods commonly used to secure online access:
Two-factor authentication (2FA)
Two-factor authentication adds an extra layer of security by requiring not only a password and username, but also something that only the user possesses, such as a physical token or an SMS message sent to their cell phone.
Multi-factor authentication (MFA)
Multi-factor authentication enhances security by requiring more than two separate authentication elements. This could include elements such as biometric recognition or electronic signature to ensure the person’s identity.
Biometric fingerprint authentication
Biometric data unique to each individual, such as fingerprints, facial recognition or iris GRC, are used to verify the user’s identity. This form of authentication is both practical and extremely difficult to forge.
The challenges of digital authentication
Digital authentication also presents its own set of challenges, particularly with regard to privacy and the management of personal data. Standards such as the GDPR in Europe have been established to regulate its use. The CNIL thus notes that the processing of biometric data intended to automatically and uniquely identify an individual based on their physical, physiological, or behavioral characteristics constitutes the processing of sensitive data, which falls under Article 9 of the GDPR—a provision that directly applies to biometric authentication (CNIL, Security: Authenticating Users).
Technological developments
As technology continues to evolve, digital authentication is turning to advanced solutions such as artificial intelligence, involving legal analytics systems capable of learning and adapting to users’ login behavior.
Practical applications in a legal environment
eDiscovery, contract lifecycle management and smart contracts are just some of the legal applications that benefit from digital authentication, securing processes and helping to automate the law.
Crucial role in cybersecurity
Digital authentication is the first line of defense against cyberattacks. By verifying users’ identities, companies can prevent many malicious intrusions, thereby protecting their critical resources. The French regulatory framework provides a concrete example of this in the payments sector: the Monetary and Financial Code requires payment service providers to implement strong customer authentication when a payer accesses their online payment account or initiates an electronic payment transaction, particularly via a remote communication channel exposed to a risk of fraud (Article L. 133-44).
Frequently asked questions
Here is a list of frequently asked questions about digital authentication.
Why is it important to diversify authentication methods?
Diversifying authentication methods improves security. If one method is compromised, the others will still act as a barrier to prevent unauthorized access.
What makes biometric authentication reliable?
Biometric authentication is reputedly reliable because it is based on characteristics unique to the individual, such as fingerprints or face, which are very difficult to reproduce or steal.
What role does artificial intelligence play in digital authentication?
Artificial intelligence can learn users’ usual access patterns and alert them to abnormal behavior, increasing the security and responsiveness of authentication systems.
How do regulations impact digital authentication?
Regulations such as the GDPR require that personal data be processed securely, which includes the use of robust authentication methods to access that data. The CNIL’s recommendations on user authentication provide practical guidance on this: a unique identifier for each user, precautions regarding passwords, and the use of multi-factor authentication to strengthen access security.
In conclusion, digital authentication is not just a technical subject reserved for IT experts; it touches on various aspects of our daily online lives, and continues to evolve in response to new threats and regulatory requirements.